Security Monitoring & Operations
Security monitoring built for small teams
Detect, investigate, and respond to security events in real time with an integrated SIEM.
Why Fencer?
Security operations without the overhead
Built for startups
Monitors the systems and tools you’re using without the heavy enterprise weight
Cut to what matters
Context-aware detections find real issues in your running systems.
Instant Coverage
Connect your stack and start monitoring in minutes.
Capabilities
Security operations, simplified
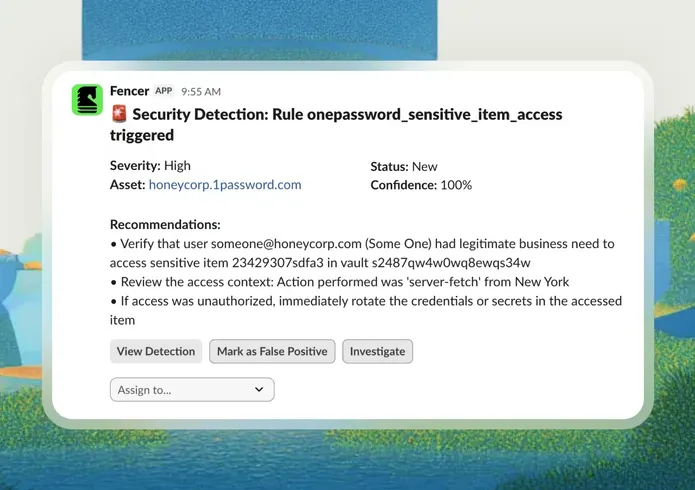
Security Detection & Alerting
Know when something’s wrong
Always on threat detection alerts you to suspicious activity and potential intrusions in GitHub, AWS, 1Password, and more.
Security Event Observability
Get the context to investigate
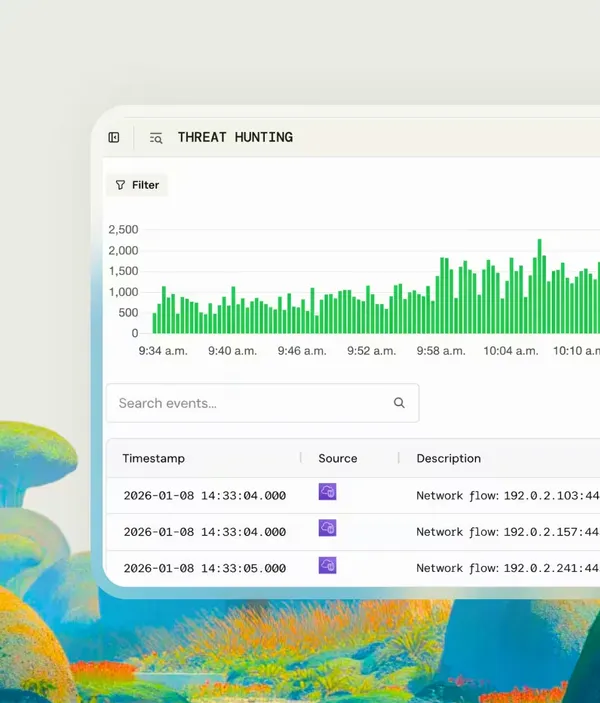
Raw event data
Access the raw events behind alerts and detections.
Real-time observability
See what happened as it unfolded.
Threat Hunting
Dig into security events with full context.
Incident Response (coming soon)
Run incident response by the book
Incident Response
Ensure incidents are handled according to your incident response plan.
Incident response tracking
Track progress from detection through resolution.
Incident documentation
Record timelines, actions, and evidence as incidents unfold.
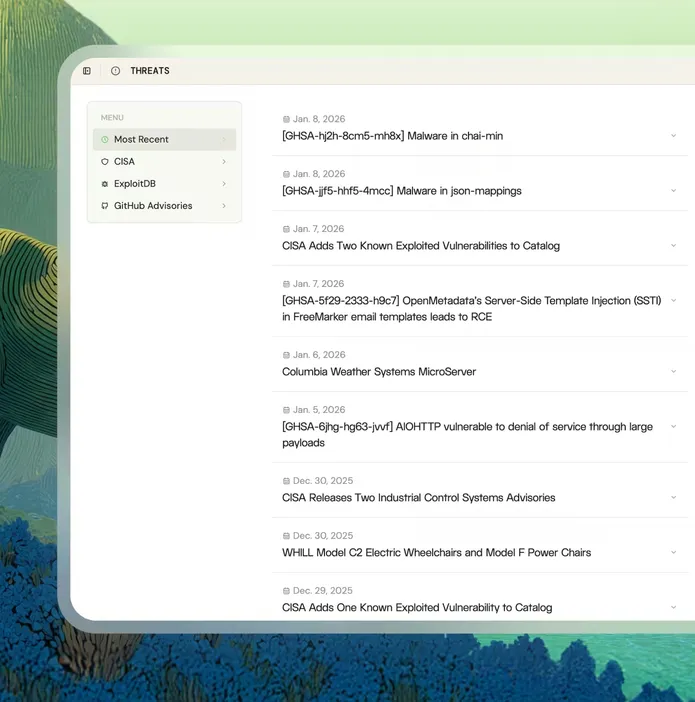
THreat Intelligence
Know what’s happening beyond your stack
Stay ahead of industry-wide security threats.

“Before Fencer, there was a lot of day-to-day anxiety around unknown security risks. Now we have confidence that those risks are being monitored and surfaced.”
— Jason Byck
CTO, Renew
Take Fencer for a spin
See what security handled from code to cloud looks like.
Start a free trial in minutes, or book a demo for a guided tour.
Start a free trial in minutes, or book a demo for a guided tour.